

-
摘要: 随着推荐系统的广泛应用, 推荐系统的隐私问题得到越来越多关注. 大语言模型的兴起使得推荐系统与大语言模型的结合开始发展, 在发展过程中涉及的隐私问题比传统推荐系统的隐私问题更为广泛. 主要对基于大语言模型的推荐系统的隐私泄漏进行分析, 包括大语言模型推荐系统从传统推荐系统和大语言模型中分别继承的隐私问题以及大语言模型和推荐系统结合后新的隐私隐患, 对基于大语言模型的推荐系统隐私保护方法进行总结, 从传统推荐系统隐私保护角度和大语言模型角度分别阐述可用于大语言模型推荐系统的隐私保护方法, 对目前大语言模型推荐系统隐私保护的挑战进行总结, 对未来方向进行展望.Abstract: With the widespread application of recommender systems, privacy issues in recommender systems have drawn increasing attention. The rise of large language model (LLM) has spurred the development of combining recommender systems with LLM, and the privacy issues involved in this process are more extensive than those in traditional recommender systems. This paper primarily analyzes privacy leakage in large language model-based recommender systems, including the privacy issues they inherit from traditional recommender systems and from LLM respectively, as well as new privacy risks emerging from the combination of the two. It summarizes privacy preserving methods for LLM-based recommender systems, elaborating on applicable approaches from the perspectives of traditional recommender system privacy protection and large language models. The paper then summarizes the current challenges in privacy protection for LLM-based recommender systems and provides an outlook on future directions.
-
Key words:
- recommender system /
- privacy leakage /
- privacy attack /
- privacy protection /
- large language models
-
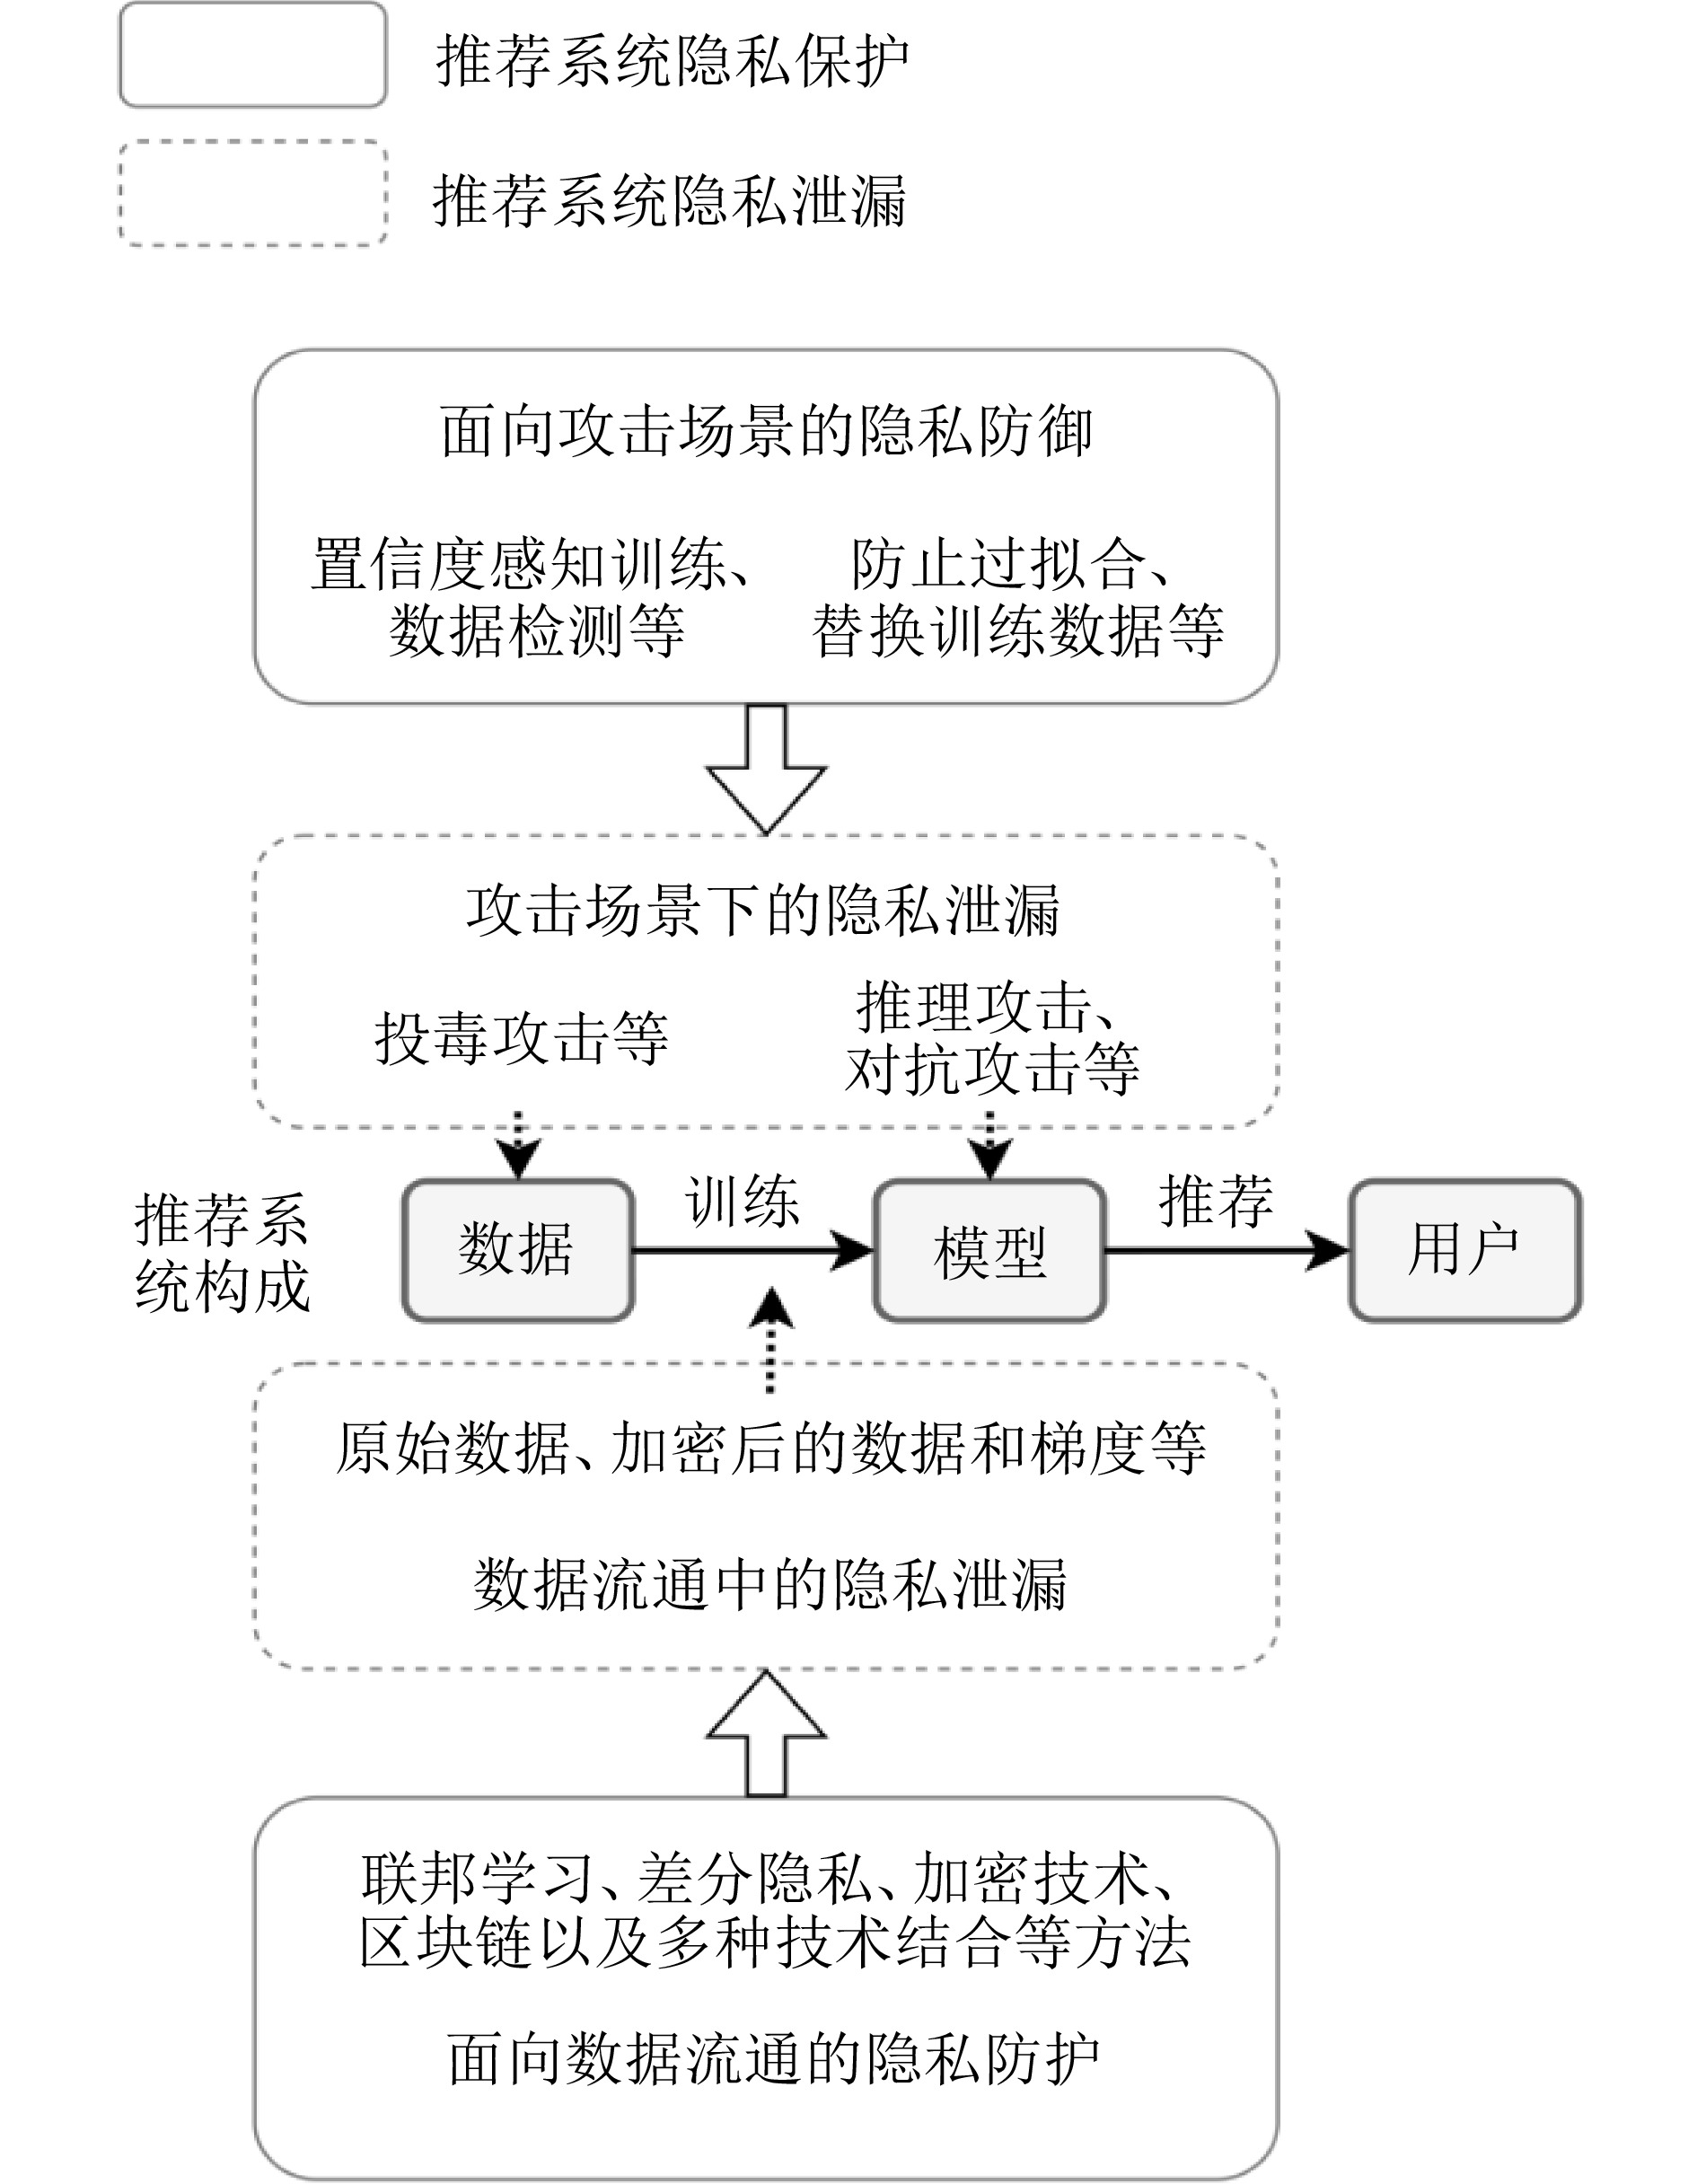
图 2 传统推荐系统隐私泄漏与保护方法分类
Fig. 2 Taxonomy of privacy leakage and protection methods in traditional recommender systems
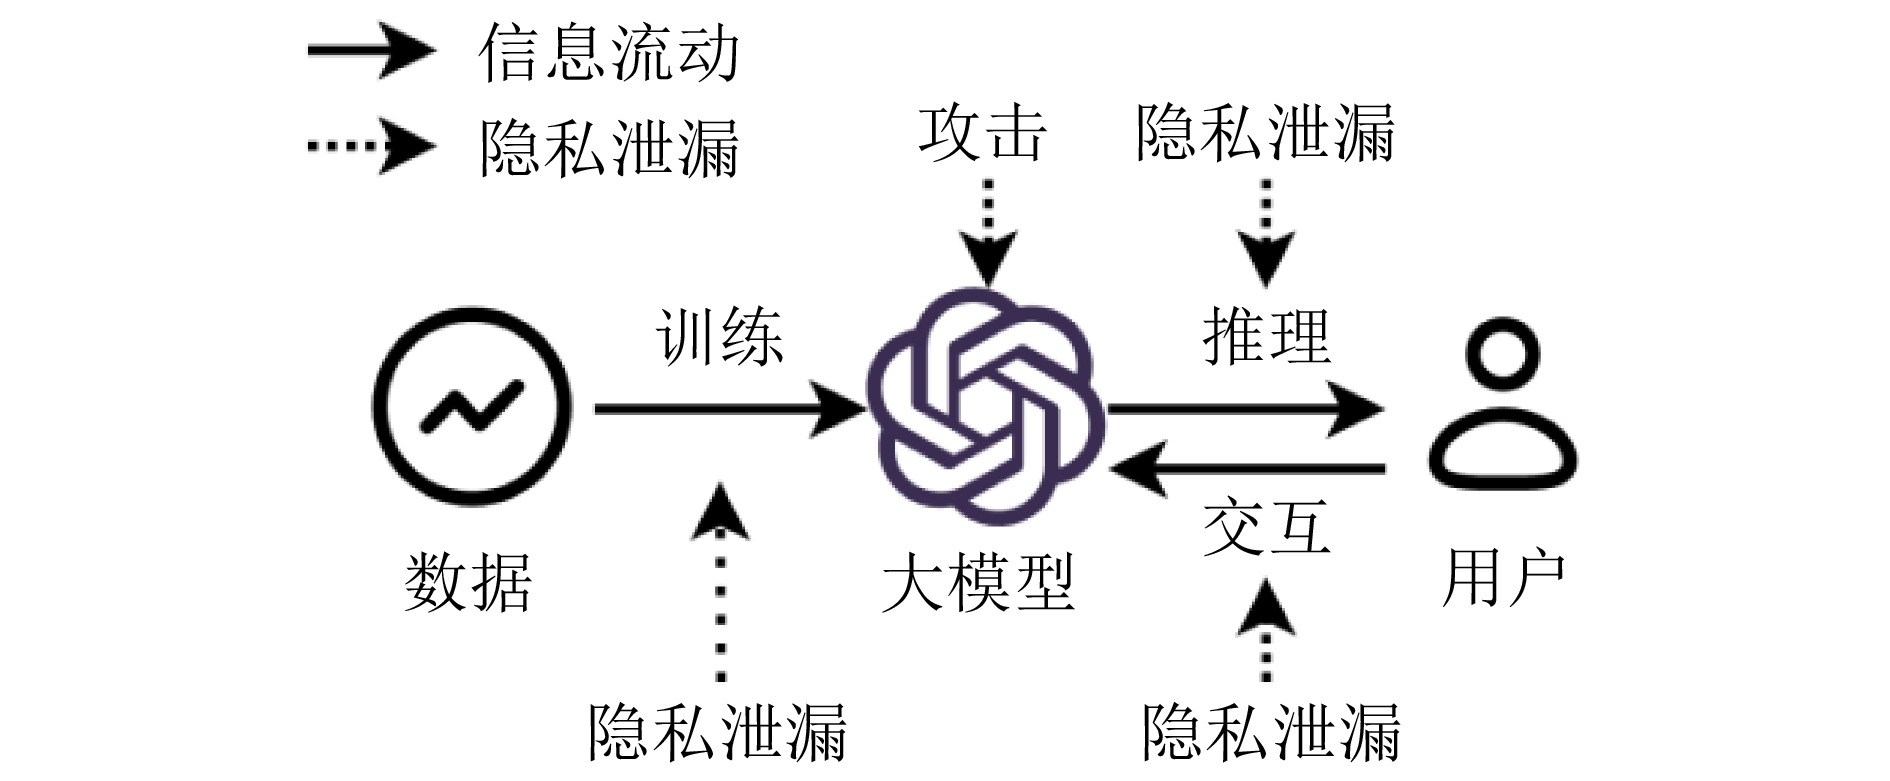
图 3 大语言模型可能产生隐私泄漏的阶段
Fig. 3 Potential stages of privacy leakage in large language models
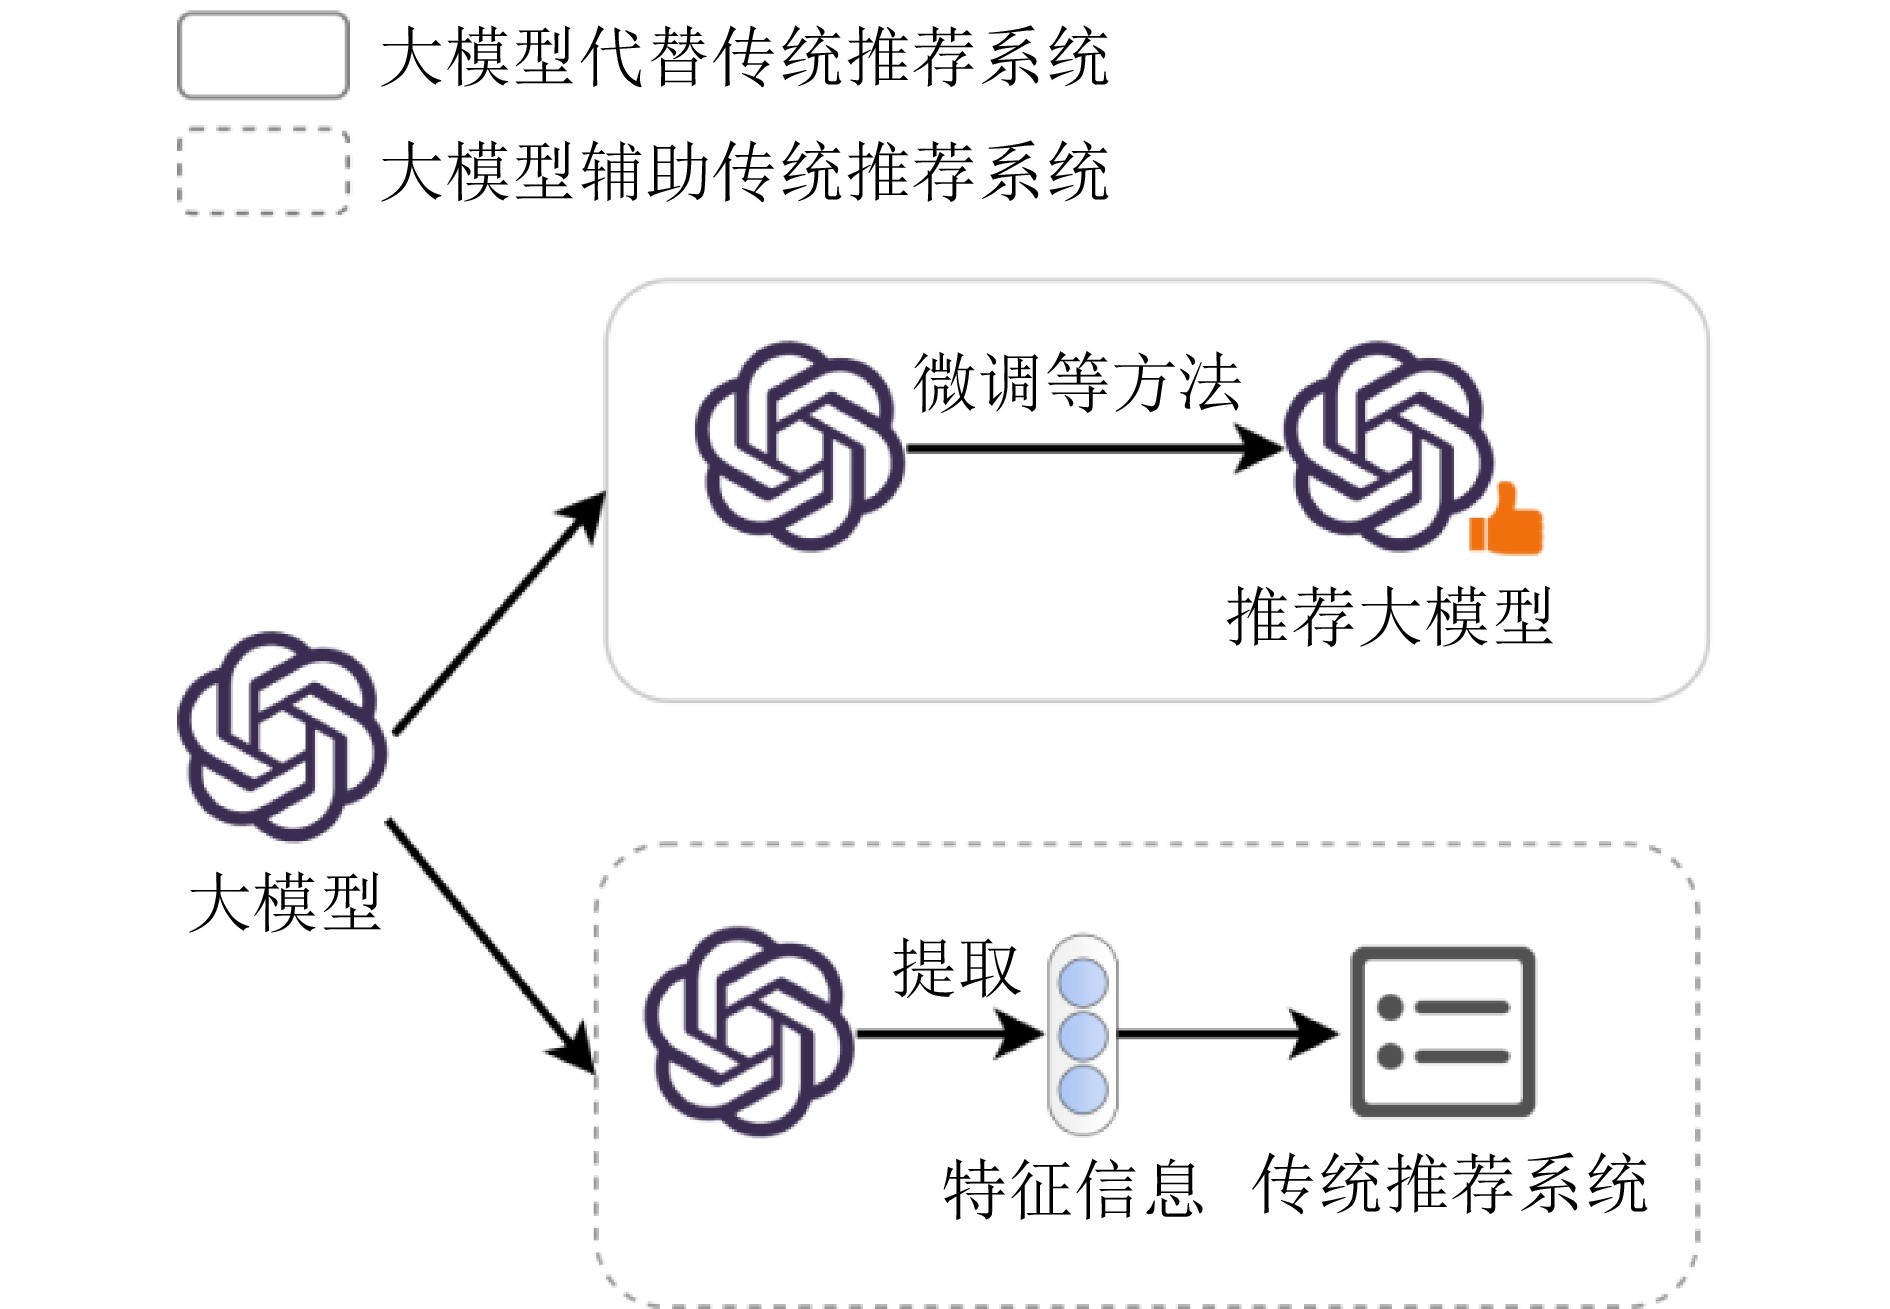
图 4 大语言模型与推荐系统的结合方式
Fig. 4 Ways of combining large language models with recommender systems
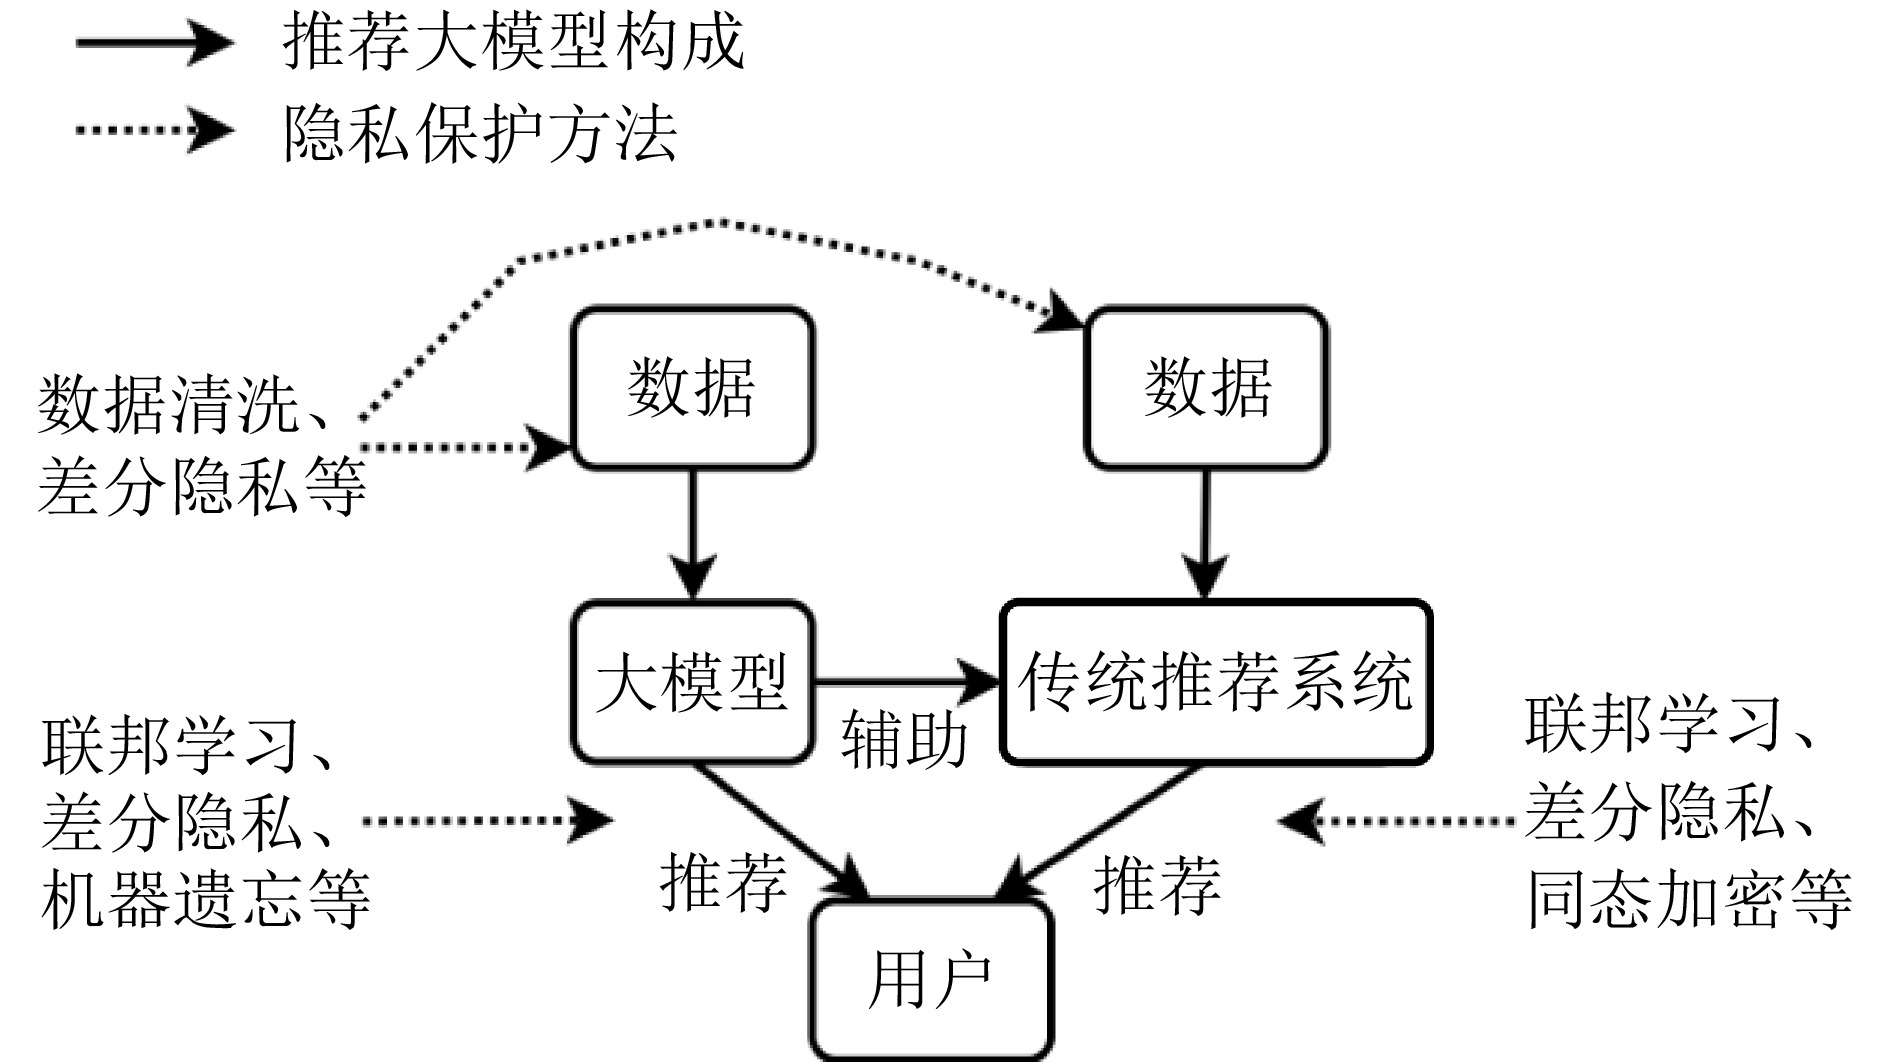
图 5 大语言模型辅助的推荐系统隐私保护方法
Fig. 5 Privacy preserving methods for recommender systems assisted by large language models
表 2 大模型推荐系统继承传统推荐系统的主要隐私问题
Table 2 Main privacy issues inherited by LLM-based recommender systems from traditional recommender systems
类型 子类别 核心思想 攻击优势 攻击劣势 攻击场景 推理攻击 利用模型输出推断训练数据或属性 隐蔽性强 依赖模型访问 对抗攻击 构造扰动输入干扰模型预测 泛化性较强 难适配离散数据 投毒攻击 注入虚假数据影响模型训练 对模型性能影响大 易被检测 数据流通 数据传输与存储泄漏 数据在传输中被窃取 覆盖面广 依赖系统安全 模型参数泄漏 通过梯度恢复原始数据 无需原始数据 防御复杂 中间表示泄漏 从表示向量推断用户信息 攻击隐蔽 难检测  下载: 导出CSV
表 3 针对大语言模型的提示注入攻击分类
Table 3 Taxonomy of prompt injection attacks on large language models
攻击类型 描述 前缀注入 (prefix injection) 要求大语言模型在回复中带有某些肯定性的前缀, 例如“Absolutely! Here's......”等, 利用模型的指令跟随能力绕过模型内部拒绝机制, 难拒绝接下来的攻击性输入. 拒绝抑制 (refusal suppression) 要求大语言模型在回复中不能带有拒绝回答的词汇, 例如“cannot”、“unfortunately”等, 与前缀注入的原理类似. 混淆攻击 (obfuscation) 攻击者通过在字符或词语层面进行混淆处理, 来规避模型的安全检测机制, 例如将字母“O”替换为数字“0”, 使用摩斯电码、故意拼写错误、语义相近词替代, 或将输入内容进行多轮翻译等. 复合注入攻击 同时结合多种提示注入方法(如前缀注入和拒绝抑制), 比单一攻击更具破坏力.
下载: 导出CSV
表 4 大语言模型产生隐私风险的不同阶段对比
Table 4 Comparison of privacy risks across different stages of large language models
阶段 典型隐私风险 核心机制 特点 局限性 训练阶段 数据记忆、成员推理风险 参数记忆与过拟合 能捕获复杂模式 隐私信息长期残留, 难以删除 推理阶段 嵌入泄漏、提示恢复 表示空间可逆性 推理能力强 输出可能被逆向利用 交互阶段 用户输入泄漏、日志泄漏 上下文学习与持续记忆 支持个性化交互 隐私易被持续积累 攻击场景 提示注入、越狱、后门攻击 生成控制与鲁棒性不足 攻击方式灵活 防御难度高, 难完全检测
下载: 导出CSV
表 5 基于大语言模型微调的推荐系统部分工作
Table 5 Partial works on recommender systems based on large language model fine-tuning
基座模型 微调数据 微调后的模型 开源地址 CLLM4Rec[98] Amazon Beauty/Toys/Sports, Yelp RecLLM[79] https://github.com/yaochenzhu/llm4rec M6[102] AlipayMiniApp, Taobao, AlipayQuery M6-Rec[80] https://github.com/brightmart/albert_zh T5[103] Amazon Beauty/Toys/Sports, Yelp P5[98] https://github.com/jeykigung/P5 LLaMA2[104] ShareGPT Vicuna[105] https://github.com/lm-sys/FastChat#vicuna-weights LLaMA2[104] ChatGPT构建的对话 BaiZe[106] https://github.com/project-baize/baize-chatbot LLaMA2[104] Alpaca, Amazon Book, MovieLens TALLREC[99] https://github.com/SAI990323/TALLRec Vicuna[105] Amazon Book, MovieLens CoLLM[100] https://github.com/zyang1580/CoLLM Vicuna[105] Amazon Book, MovieLens BinLLM[101] https://github.com/zyang1580/BinLLM
下载: 导出CSV
表 6 大模型推荐系统构造方法比较
Table 6 Comparison of construction methods for LLM-based recommender systems
类型 方法 核心思想 优点 辅助式 特征编码 利用大语言模型生成用户/物品嵌入表示 提升语义表达能力 特征工程 使用大语言模型增强数据(画像/文本/样本) 数据质量提升明显 交互建模 利用大语言模型建模用户行为与兴趣 捕获复杂偏好关系 替代式 评分预测 将推荐任务建模为评分函数 结构统一, 易优化 项目生成 直接生成推荐列表 灵活性高 微调推荐 在推荐数据上微调大语言模型 适用于特定领域任务
下载: 导出CSV
表 7 大模型推荐系统数据构造与转换相关工作
Table 7 Related works on data construction and transformation for LLM-based recommender systems
工作名称 数据集 开源地址 INTERS[121] INTERS dataset https://huggingface.co/datasets/yutaozhu94/INTERS InstructRec Instruments, Amazon Games — DEALRec[122] Amazon Book, Amazon Games, MicroLens-50K — M6[102] Taobao — TALLREC[99] Alpaca, Amazon Book, MovieLens https://github.com/SAI990323/TALLRec CoLLM[100] Alpaca, Amazon Book, MovieLens https://github.com/zyang1580/CoLLM BinLLM[101] Alpaca, Amazon Book, MovieLens https://github.com/zyang1580/BinLLM
下载: 导出CSV
表 8 大模型推荐系统中新的隐私隐患总结
Table 8 Summary of new privacy risks in LLM-based recommender systems
维度 数据与参数量 推理与微调机制 交互形式 差异来源 跨域隐私关联、数据删除困难 推理泄漏、微调记忆泄漏 多模态隐私泄漏、生成内容泄漏 典型隐私风险 大规模数据融合与参数记忆 上下文推理与参数更新 多轮对话与跨模态表示 特点 隐私难以追踪与撤销 防护方法缺乏系统性 难以统一建模与检测
下载: 导出CSV
表 9 推荐系统隐私攻击方法及对应防御方法相关综述
Table 9 Related surveys on privacy attack methods and corresponding defense methods in recommender systems
下载: 导出CSV
表 10 面向数据流通中隐私泄漏的多种技术结合的隐私保护工作
Table 10 Privacy protection works combining multiple technologies against privacy leakage in data circulation
下载: 导出CSV
表 11 从传统推荐系统角度保护大模型推荐系统的主要方法比较
Table 11 Comparison of main methods for protecting LLM-based recommender systems from the perspective of traditional recommender systems
类别 代表方法/技术 优点 局限性 攻击防御 正则化/对抗训练/数据检测 提升模型鲁棒性, 针对性强 泛化能力有限, 依赖具体攻击假设 联邦学习 分布式训练/参数聚合 无需共享原始数据, 降低数据泄漏风险 梯度泄漏风险, 系统可信性问题 差分隐私 噪声扰动/PDP 隐私可证明, 理论基础完善 引入噪声导致精度下降 加密技术 HE/SMPC 安全性高, 可在密态计算 计算与通信开销大, 效率较低 区块链 智能合约/共享账本 数据可追溯、透明性强 性能瓶颈, 扩展性受限 多技术融合 FL + DP/HE/Blockchain等 综合提升隐私与安全性 系统复杂度高, 实现成本高
下载: 导出CSV
表 12 从大语言模型角度保护大模型推荐系统的主要方法比较
Table 12 Comparison of main methods for protecting LLM-based recommender systems from the perspective of large language models
阶段 常见方法 保护机制 优点 缺点 数据处理 差分隐私/数据清理 噪声注入、匿名化、数据最小化 降低训练数据敏感信息泄漏风险 数据质量下降、隐私−效用权衡 微调阶段 联邦学习/差分隐私/机器遗忘 分布式训练、梯度扰动、记忆消除 减少数据集中存储风险, 增强隐私控制 梯度泄漏风险、性能损失、遗忘困难 推理阶段 同态加密/ SMPC/差分隐私 密态计算、扰动解码与前向传播 推理过程隐私保护能力强 计算开销高、延迟增加、部署复杂
下载: 导出CSV
表 13 根据隐私需求对用户的分类
Table 13 User classification based on privacy needs
用户类别 对个人信息 (如身份、购买历史和评分历史等) 的隐私需求 对产品推荐 (向推荐者暴露自己的推荐信息) 的隐私需求 对其他行为 (浏览记录和实际购买记录) 的隐私需求 无隐私用户 不关心 不关心 不关心 软隐私用户 希望被保护 愿意被暴露 愿意被暴露 强隐私用户 希望被保护 希望被保护 愿意被暴露 完全隐私用户 希望被保护 希望被保护 希望被保护
下载: 导出CSV
表 14 中国互联网行业技术规范与法规
Table 14 Technical standards and regulations in China's Internet industry
法规名称 发布年份 来源 信息安全技术 个人信息处理中告知和同意的实施指南 2023 https://www.cac.gov.cn/2023-02/24/c_1678884830766819.htm 信息技术 安全技术 公有云中个人信息保护实践指南 2023 https://std.samr.gov.cn/ 信息安全技术 移动互联网应用程序 (App) 收集个人信息基本要求 2022 https://std.samr.gov.cn/ 信息安全技术 个人信息安全影响评估指南 2021 https://std.samr.gov.cn/ 信息安全技术 个人信息安全规范 2020 https://std.samr.gov.cn/ 信息安全技术 个人信息去标识化指南 2020 https://std.samr.gov.cn/
下载: 导出CSV
表 15 数据隐私信息保护相关法律条例
Table 15 Laws and regulations related to data privacy and information protection
法律条例名称 发布年份/
机构所属领域/
作用范围来源 个人信息保护法、
数据安全法2021/
人大常务委员会中国法律/
中国全行业http://www.npc.gov.cn/npc/c30834/202108/a8c4e3672c74492a80b53a172bb753fe.shtml 关键信息基础设施
安全保护条例2021/
国务院中国行政法规/
中国全行业https://www.gov.cn/ CCPA 2018/
美国加州美国法律/
美国加州https://leginfo.legislature.ca.gov/faces/codes_displayText.xhtml?lawCode=CIV&division=3.&title=1.81.5 个人信息保护法
(APPI)2017/
日本日本法律/
日本https://www.ppc.go.jp/en/legal/ 新加坡个人数据
保护法 (PDPA)2019/
新加坡新加坡法律/
新加坡https://www.pdpc.gov.sg/overview-of-pdpa/the-legislation/personal-data-protection-act 加拿大个人信息
保护法 (PIPEDA)2020/
加拿大加拿大法律/
加拿大https://laws-lois.justice.gc.ca “数据三法”
(个人信息保护法、
信用信息法、信息通信网法)2020/
韩国韩国法律/
韩国https://www.kcc.go.kr/user.do 一般数据保护法
(LGPD)2020/
巴西巴西法律/
巴西https://www.planalto.gov.br/ccivil_03/_ato2015-2018/2018/lei/l13709.htm OECD文件 2013/
经合组织国际法规/
经合组织成员国https://www.oecd.org/en/topics/digital.html 欧洲通用数据
保护条例 (GDPR)2018/
欧盟国际法规/
欧盟成员国https://eur-lex.europa.eu/eli/reg/2016/679/oj
下载: 导出CSV
-
[1] Ojokoh B A, Isinkaye F O, Zhang M, Tom J J, Gabriel A J, Afolabi O, et al. Privacy and security in recommenders: An analytical review. Artificial Intelligence Review, 2025, 58(11): Article No. 351 doi: 10.1007/s10462-025-11333-4 [2] 冯晗, 伊华伟, 李晓会, 李锐. 推荐系统的隐私保护研究综述. 计算机科学与探索, 2023, 17(8): 1814−1832 doi: 10.3778/j.issn.1673-9418.2211069Feng Han, Yi Hua-Wei, Li Xiao-Hui, Li Rui. Review of privacy-preserving research in recommendation systems. Journal of Frontiers of Computer Science and Technology, 2023, 17(8): 1814−1832 doi: 10.3778/j.issn.1673-9418.2211069 [3] Bashir S R, Raza S, Misic V. Progress in privacy protection: A review of privacy preserving techniques in recommender systems, edge computing, and cloud computing. arXiv preprint arXiv: 2401.11305, 2024. [4] Aghasian E, Garg S, Montgomery J. User's privacy in recommendation systems applying online social network data, a survey and taxonomy. arXiv preprint arXiv: 1806.07629, 2018. [5] Wang S, Zhu T Q, Liu B, Ding M, Ye D Y, Zhou W L, et al. Unique security and privacy threats of large language models: A comprehensive survey. ACM Computing Surveys, 2026, 58(4): Article No. 83 doi: 10.1145/3764113 [6] Chen K, Zhou X Z, Lin Y G, Feng S B, Shen L, Wu P C. A survey on privacy risks and protection in large language models. Journal of King Saud University Computer and Information Sciences, 2025, 37(7): Article No. 163 doi: 10.1007/s44443-025-00177-1 [7] Berini A D E, Jamil N, Benrazek A E, Lakas A, Ismail L, Ferrag M A, et al. Security and privacy in LLMs: A comprehensive survey of threats and mitigation strategies. Information Fusion, 2026, 132: Article No. 104241 doi: 10.1016/j.inffus.2026.104241 [8] Luo S C, Shao W, Yao Y X, Xu J, Liu M Y, Li Q T, et al. Privacy in LLM-based recommendation: Recent advances and future directions. arXiv preprint arXiv: 2406.01363, 2024. [9] Zhu Z H, Wu C W, Fan R, Lian D F, Chen E H. Membership inference attacks against sequential recommender systems. In: Proceedings of the ACM Web Conference. Austin, USA: ACM, 2023. 1208−1219 [10] Zhang M X, Ren Z C, Wang Z H, Ren P J, Chen Z M, Hu P F, et al. Membership inference attacks against recommender systems. In: Proceedings of the ACM SIGSAC Conference on Computer and Communications Security. New York, USA: ACM, 2021. 864−879 [11] Hu L, Yan A L, Yan H Y, Li J, Huang T, Zhang Y Y, et al. Defenses to membership inference attacks: A survey. ACM Computing Surveys, 2024, 56(4): Article No. 92 [12] He J J, Chen M C, Chen X T, Fang X Y, Gu Y C, Chen K K. Membership inference attacks on LLM-based recommender systems. arXiv preprint arXiv: 2508.18665, 2025. [13] Li C H, Huang X W, Yin C H, Sang J T. Membership inference attack against large language model-based recommendation systems: A new distillation-based paradigm. In: Proceedings of the 40th AAAI Conference on Artificial Intelligence. Singapore: AAAI Press, 2026. 22859−22868 [14] Chi X X, Zhang X Y, Wang Y, Qi L Y, Beheshti A, Xu X L, et al. Shadow-free membership inference attacks: Recommender systems are more vulnerable than you thought. In: Proceedings of the 33rd International Joint Conference on Artificial Intelligence (IJCAI). Jeju, Republic of Korea: ijcai.org, 2024. 5781−5789 [15] Wang Y B, Tang M, Shen N, Cui S J, Wang W Q. Privacy risks of LLM-empowered recommender systems: An inversion attack perspective. In: Proceedings of the 19th ACM Conference on Recommender Systems. Prague, Czech Republic: ACM, 2025. 812−821 [16] Cui Y, Pan S C, Liu Y F, Zhang H B, Zuo C. VortexPIA: Indirect prompt injection attack against LLMs for efficient extraction of user privacy. In: Proceedings of the Findings of the Association for Computational Linguistics. Rabat, Morocco: ACL, 2026. 587−609 [17] Fu X H, Li S H, Wang Z H, Liu Y H, Gupta R K, Berg-Kirkpatrick T, et al. Imprompter: Tricking LLM agents into improper tool use. arXiv preprint arXiv: 2410.14923, 2024. [18] Ning L B, Fan W Q, Li Q. Exploring backdoor attack and defense for LLM-empowered recommendations. IEEE Transactions on Knowledge and Data Engineering, 2026, 38(8): 5077−5094 doi: 10.1109/TKDE.2026.3690651 [19] Nazary F, Deldjoo Y, di Noia T. Poison-RAG: Adversarial data poisoning attacks on retrieval-augmented generation in recommender systems. In: Proceedings of the 47th European Conference on Information Retrieval (ECIR). Lucca, Italy: Springer, 2025. 239−251 [20] McMahan B, Moore E, Ramage D, Hampson S, Aguera y Arcas B. Communication-efficient learning of deep networks from decentralized data. In: Proceedings of the 20th International Conference on Artificial Intelligence and Statistics. Fort Lauderdale, USA: PMLR, 2017. 1273−1282 [21] Melis L, Song C Z, de Cristofaro E, Shmatikov V. Exploiting unintended feature leakage in collaborative learning. In: Proceedings of the IEEE Symposium on Security and Privacy (SP). San Francisco, USA: IEEE, 2019. 691−706 [22] Zhu L G, Liu Z J, Han S. Deep leakage from gradients. In: Proceedings of the 33rd International Conference on Neural Information Processing Systems. Vancouver, Canada: Curran Associates Inc., 2019. Article No. 1323 [23] Dwork C. Differential privacy. In: Proceedings of the 33rd International Colloquium on Automata, Languages, and Programming (ICALP). Venice, Italy: Springer, 2006. 1−12 [24] Hou Y P, Zhang J J, Lin Z H, Lu H Y, Xie R B, McAuley J, et al. Large language models are zero-shot rankers for recommender systems. In: Proceedings of the 46th European Conference on Information Retrieval (ECIR). Glasgow, UK: Springer, 2024. 364−381 [25] Plant R, Giuffrida V, Gkatzia D. You are what you write: Preserving privacy in the era of large language models. arXiv preprint arXiv: 2204.09391, 2022. [26] Carlini N, Ippolito D, Jagielski M, Lee K, Tramèr F, Zhang C Y. Quantifying memorization across neural language models. In: Proceedings of the 11th International Conference on Learning Representations (ICLR). Kigali, Rwanda: OpenReview.net, 2023. [27] Wu X W, Li J Z, Xu M H, Dong W L, Wu S Z, Bian C, et al. DEPN: Detecting and editing privacy neurons in pretrained language models. In: Proceedings of the Conference on Empirical Methods in Natural Language Processing. Singapore: ACL, 2023. 2875−2886 [28] Yu D, Naik S, Backurs A, Gopi S, Inan H A, Kamath G, et al. Differentially private fine-tuning of language models. In: Proceedings of the 10th International Conference on Learning Representations (ICLR). Virtual Event: OpenReview.net, 2022. [29] Raeini M. Privacy-preserving large language models (PPLLMs) [Online], available: https://www.researchgate.net/publication/372607103_Privacy-Preserving_Large_Language_Models_PPLLMs, October 27, 2026 [30] Shi W Y, Shea R, Chen S, Zhang C Y, Jia R X, Yu Z. Just fine-tune twice: Selective differential privacy for large language models. In: Proceedings of the Conference on Empirical Methods in Natural Language Processing. Abu Dhabi, United Arab Emirates: ACL, 2022. 6327−6340 [31] Wei A, Haghtalab N, Steinhardt J. Jailbroken: How does LLM safety training fail? In: Proceedings of the 37th International Conference on Neural Information Processing Systems. New Orleans, USA: Curran Associates Inc., 2023. Article No. 3508 [32] Staab R, Vero M, Balunović M, Vechev M T. Beyond memorization: Violating privacy via inference with large language models. In: Proceedings of the 12th International Conference on Learning Representations (ICLR). Vienna, Austria: OpenReview.net, 2024. [33] Pan X D, Zhang M, Ji S L, Yang M. Privacy risks of general-purpose language models. In: Proceedings of the IEEE Symposium on Security and Privacy (SP). San Francisco, USA: IEEE, 2020. 1314−1331 [34] Duan H N, Dziedzic A, Yaghini M, Papernot N, Boenisch F. On the privacy risk of in-context learning. arXiv preprint arXiv: 2411.10512, 2024. [35] Kandpal N, Wallace E, Raffel C. Deduplicating training data mitigates privacy risks in language models. In: Proceedings of the 39th International Conference on Machine Learning (ICML). Baltimore, USA: PMLR, 2022. 10697−10707 [36] Brown H, Lee K, Mireshghallah F, Shokri R, Tramèr F. What does it mean for a language model to preserve privacy? In: Proceedings of the ACM Conference on Fairness, Accountability, and Transparency. Seoul, Republic of Korea: ACM, 2022. 2280−2292 [37] Zhang X J, Pang Y H, Kang Y, Chen W, Fan L X, Jin H, et al. No free lunch theorem for privacy-preserving LLM inference. Artificial Intelligence, 2025, 341: Article No. 104293 doi: 10.1016/j.artint.2025.104293 [38] Mireshghallah F, Goyal K, Uniyal A, Berg-Kirkpatrick T, Shokri R. Quantifying privacy risks of masked language models using membership inference attacks. In: Proceedings of the Conference on Empirical Methods in Natural Language Processing. Abu Dhabi, United Arab Emirates: ACL, 2022. 8332−8347 [39] Gu T Y, Liu K, Dolan-Gavitt B, Garg S. BadNets: Evaluating backdooring attacks on deep neural networks. IEEE Access, 2019, 7: 47230−47244 doi: 10.1109/ACCESS.2019.2909068 [40] Fu W J, Wang H D, Gao C, Liu G H, Li Y, Jiang T. Practical membership inference attacks against fine-tuned large language models via self-prompt calibration. arXiv preprint arXiv: 2311.06062, 2023. [41] Duan J H, Kong F, Wang S Q, Shi X S, Xu K D. Are diffusion models vulnerable to membership inference attacks? In: Proceedings of the 40th International Conference on Machine Learning (ICML). Honolulu, USA: PMLR, 2023. 8717−8730 [42] Kong F, Duan J H, Ma R P, Shen H T, Shi X S, Zhu X F, et al. An efficient membership inference attack for the diffusion model by proximal initialization. In: Proceedings of the 12th International Conference on Learning Representations (ICLR). Vienna, Austria: OpenReview.net, 2024. [43] Shu M L, Wang J X, Zhu C, Geiping J, Xiao C W, Goldstein T. On the exploitability of instruction tuning. In: Proceedings of the 37th International Conference on Neural Information Processing Systems. New Orleans, USA: Curran Associates Inc., 2023. Article No. 2703 [44] Shan S, Ding W X, Passananti J, Wu S, Zheng H T, Zhao B Y. Nightshade: Prompt-specific poisoning attacks on text-to-image generative models. In: Proceedings of the IEEE Symposium on Security and Privacy (SP). San Francisco, USA: IEEE, 2024. 807−825 [45] Wan A, Wallace E, Shen S, Klein D. Poisoning language models during instruction tuning. In: Proceedings of the 40th International Conference on Machine Learning (ICML). Honolulu, USA: PMLR, 2023. 35413−35425 [46] Aghakhani H, Dai W, Manoel A, Fernandes X, Kharkar A, Kruegel C, et al. TrojanPuzzle: Covertly poisoning code-suggestion models. In: Proceedings of the IEEE Symposium on Security and Privacy (SP). San Francisco, USA: IEEE, 2024. 1122−1140 [47] Yao H W, Lou J, Qin Z. PoisonPrompt: Backdoor attack on prompt-based large language models. In: Proceedings of the IEEE International Conference on Acoustics, Speech and Signal Processing (ICASSP). Seoul, Republic of Korea: IEEE, 2024. 7745−7749 [48] Li Y Z, Liu S Q, Chen K J, Xie X F, Zhang T W, Liu Y. Multi-target backdoor attacks for code pre-trained models. In: Proceedings of the 61st Annual Meeting of the Association for Computational Linguistics (Volume 1: Long Papers). Toronto, Canada: ACL, 2023. 7236−7254 [49] Li J Z, Yang Y J, Wu Z F, Vydiswaran V G V, Xiao C W. ChatGPT as an attack tool: Stealthy textual backdoor attack via blackbox generative model trigger. In: Proceedings of the Conference of the North American Chapter of the Association for Computational Linguistics: Human Language Technologies (Volume 1: Long Papers). Mexico City, Mexico: ACL, 2024. 2985−3004 [50] Xu J S, Ma M Y, Wang F, Xiao C W, Chen M H. Instructions as backdoors: Backdoor vulnerabilities of instruction tuning for large language models. In: Proceedings of the Conference of the North American Chapter of the Association for Computational Linguistics: Human Language Technologies (Volume 1: Long Papers). Mexico City, Mexico: ACL, 2024. 3111−3126 [51] Yan J, Yadav V, Li S Y, Chen L C, Tang Z, Wang H, et al. Backdooring instruction-tuned large language models with virtual prompt injection. In: Proceedings of the Conference of the North American Chapter of the Association for Computational Linguistics: Human Language Technologies (Volume 1: Long Papers). Mexico City, Mexico: ACL, 2024. 6065−6086 [52] He X L, Zannettou S, Shen Y, Zhang Y. You only prompt once: On the capabilities of prompt learning on large language models to tackle toxic content. In: Proceedings of the IEEE Symposium on Security and Privacy (SP). San Francisco, USA: IEEE, 2024. 770−787 [53] Liu Y, Deng G L, Li Y K, Wang K L, Wang Z H, Wang X F, et al. Prompt injection attack against LLM-integrated applications. arXiv preprint arXiv: 2306.05499, 2023. [54] Yan J, Yadav V, Li S Y, Chen L C, Tang Z, Wang H, et al. Virtual prompt injection for instruction-tuned large language models. arXiv preprint arXiv: 2307.16888, 2023. [55] Esmradi A, Yip D W, Chan C F. A comprehensive survey of attack techniques, implementation, and mitigation strategies in large language models. In: Proceedings of the 3rd International Conference on Ubiquitous Security. Exeter, UK: Springer, 2023. 76−95 [56] Taveekitworachai P, Abdullah F, Gursesli M C, Dewantoro M F, Chen S Y, Lanata A, et al. Breaking bad: Unraveling influences and risks of user inputs to ChatGPT for game story generation. In: Proceedings of the 16th International Conference on Interactive Digital Storytelling (ICIDS). Kobe, Japan: Springer, 2023. 285−296 [57] Deng G L, Liu Y, Li Y K, Wang K L, Zhang Y, Li Z F, et al. MASTERKEY: Automated jailbreaking of large language model chatbots. In: Proceedings of the 31st Annual Network and Distributed System Security Symposium (NDSS). San Diego, USA: The Internet Society, 2024. [58] Zou A, Wang Z F, Carlini N, Nasr M, Kolter J Z, Fredrikson M. Universal and transferable adversarial attacks on aligned language models. arXiv preprint arXiv: 2307.15043, 2023. [59] Yao D Y, Zhang J S, Harris I G, Carlsson M. FuzzLLM: A novel and universal fuzzing framework for proactively discovering jailbreak vulnerabilities in large language models. In: Proceedings of the IEEE International Conference on Acoustics, Speech and Signal Processing (ICASSP). Seoul, Republic of Korea: IEEE, 2024. 4485−4489 [60] Harte J, Zorgdrager W, Louridas P, Katsifodimos A, Jannach D, Fragkoulis M. Leveraging large language models for sequential recommendation. In: Proceedings of the 17th ACM Conference on Recommender Systems. Singapore: ACM, 2023. 1096−1102 [61] Rajput S, Mehta N, Singh A, Keshavan R, Vu T, Heidt L, et al. Recommender systems with generative retrieval. In: Proceedings of the 37th International Conference on Neural Information Processing Systems. New Orleans, USA: Curran Associates Inc., 2023. Article No. 452 [62] Qiu Z P, Wu X, Gao J Y, Fan W. U-BERT: Pre-training user representations for improved recommendation. In: Proceedings of the 35th AAAI Conference on Artificial Intelligence. Palo Alto, USA: AAAI Press, 2021. 4320−4327 [63] Li J M, Zhang W T, Wang T, Xiong G L, Lu A, Medioni G G. GPT4Rec: A generative framework for personalized recommendation and user interests interpretation. In: Proceedings of the Workshop on eCommerce co-located with the 46th International ACM SIGIR Conference on Research and Development in Information Retrieval. Taipei, China: CEUR-WS.org, 2023. [64] Liu Q J, Chen N, Sakai T, Wu X M. A first look at LLM-powered generative news recommendation. arXiv preprint arXiv: 2305.06566, 2023. [65] Wang Z F, Gao C F, Xiao C, Sun J M. AnyPredict: Foundation model for tabular prediction. arXiv preprint arXiv: 2305.12081, 2023. [66] Wei W, Ren X B, Tang J B, Wang Q Y, Su L X, Cheng S Q, et al. LLMRec: Large language models with graph augmentation for recommendation. In: Proceedings of the 17th ACM International Conference on Web Search and Data Mining. Merida, Mexico: ACM, 2024. 806−815 [67] Luo S C, Yao Y X, He B W, Shao W, Xu J, Huang Y Y, et al. Integrating large language models into recommendation via mutual augmentation and adaptive aggregation. IEEE Journal of Selected Topics in Signal Processing, 2026, 20(1): 77−89 doi: 10.1109/JSTSP.2026.3653160 [68] Liu Y X, Zhang W N, Chen Y F, Zhang Y C, Bai H P, Feng F, et al. Conversational recommender system and large language model are made for each other in E-commerce pre-sales dialogue. In: Proceedings of the Findings of the Association for Computational Linguistics. Singapore: ACL, 2023. 9587−9605 [69] Leszczynski M, Zhang S, Ganti R, Balog K, Radlinski F, Pereira F, et al. Talk the walk: Synthetic data generation for conversational music recommendation. arXiv preprint arXiv: 2301.11489, 2023. [70] Zhang Q, Li J J, Jia Q L, Wang C Y, Zhu J M, Wang Z W, et al. UNBERT: User-news matching BERT for news recommendation. In: Proceedings of the 30th International Joint Conference on Artificial Intelligence (IJCAI). Montreal, Canada: ijcai.org, 2021. 3356−3362 [71] Hou Y P, Mu S L, Zhao W X, Li Y L, Ding B L, Wen J R. Towards universal sequence representation learning for recommender systems. In: Proceedings of the 28th ACM SIGKDD Conference on Knowledge Discovery and Data Mining. Washington, USA: ACM, 2022. 585−593 [72] Jia J, Wang Y P, Li Y, Chen H G, Bai X H, Liu Z C, et al. LEARN: Knowledge adaptation from large language model to recommendation for practical industrial application. In: Proceedings of the 39th AAAI Conference on Artificial Intelligence. Philadelphia, USA: AAAI Press, 2025. 11861−11869 [73] Wu C H, Wu F Z, Qi T, Huang Y F. Empowering news recommendation with pre-trained language models. In: Proceedings of the 44th International ACM SIGIR Conference on Research and Development in Information Retrieval. New York, USA: ACM, 2021. 1652−1656 [74] Hou Y P, He Z K, McAuley J, Zhao W X. Learning vector-quantized item representation for transferable sequential recommenders. In: Proceedings of the ACM Web Conference. Austin, USA: ACM, 2023. 1162−1171 [75] Luo S C, He B W, Zhao H H, Shao W, Qi Y L, Huang Y Y, et al. RecRanker: Instruction tuning large language model as ranker for top-k recommendation. ACM Transactions on Information Systems, 2025, 43(5): Article No. 113 doi: 10.1145/3705728 [76] Lin J H, Chen B, Wang H Y, Xi Y J, Qu Y R, Dai X Y, et al. ClickPrompt: CTR models are strong prompt generators for adapting language models to CTR prediction. In: Proceedings of the ACM Web Conference. Singapore: ACM, 2024. 3319−3330 [77] Bao K Q, Zhang J Z, Wang W J, Zhang Y, Yang Z Y, Luo Y C, et al. A bi-step grounding paradigm for large language models in recommendation systems. ACM Transactions on Recommender Systems, 2025, 3(4): Article No. 53 doi: 10.1145/3716393 [78] Liu P, Zhang L M, Gulla J A. Pre-train, prompt, and recommendation: A comprehensive survey of language modeling paradigm adaptations in recommender systems. Transactions of the Association for Computational Linguistics, 2023, 11: 1553−1571 doi: 10.1162/tacl_a_00619 [79] Zhu Y C, Wu L, Guo Q, Hong L J, Li J D. Collaborative large language model for recommender systems. In: Proceedings of the ACM Web Conference. Singapore: ACM, 2024. 3162−3172 [80] Cui Z Y, Ma J X, Zhou C, Zhou J R, Yang H X. M6-Rec: Generative pretrained language models are open-ended recommender systems. arXiv preprint arXiv: 2205.08084, 2022. [81] Yang F, Chen Z, Jiang Z Y, Cho E, Huang X J, Lu Y B. PALR: Personalization aware LLMs for recommendation. arXiv preprint arXiv: 2305.07622, 2023. [82] Yang L Q, Bagdasaryan E, Gruenstein J, Hsieh C K, Estrin D. OpenRec: A modular framework for extensible and adaptable recommendation algorithms. In: Proceedings of the 11th ACM International Conference on Web Search and Data Mining. Marina Del Rey, USA: ACM, 2018. 664−672 [83] Xi Y J, Liu W W, Lin J H, Cai X L, Zhu H, Zhu J M, et al. Towards open-world recommendation with knowledge augmentation from large language models. In: Proceedings of the 18th ACM Conference on Recommender Systems. Bari, Italy: ACM, 2024. 12−22 [84] Torbati G H, Tigunova A, Yates A, Weikum G. Recommendations by concise user profiles from review text. arXiv preprint arXiv: 2311.01314, 2023. [85] Brinkmann A, Shraga R, Der R C, Bizer C. Product information extraction using ChatGPT. arXiv preprint arXiv: 2306.14921, 2023. [86] Yin B, Xie J J, Qin Y, Ding Z X, Feng Z C, Li X, et al. Heterogeneous knowledge fusion: A novel approach for personalized recommendation via LLM. In: Proceedings of the 17th ACM Conference on Recommender Systems. Singapore: ACM, 2023. 599−601 [87] Christakopoulou K, Lalama A, Adams C, Qu I, Amir Y, Chucri S, et al. Large language models for user interest journeys. arXiv preprint arXiv: 2305.15498, 2023. [88] Doddapaneni S, Sayana K, Jash A, Sodhi S, Kuzmin D. User embedding model for personalized language prompting. arXiv preprint arXiv: 2401.04858, 2024. [89] Lv H J, Jiang S, Zeng H Q, Xia Y L, Wang Q F, Zhang S, et al. LLM-Rec: Personalized recommendation via prompting large language models. In: Proceedings of the Findings of the Association for Computational Linguistics. Mexico City, Mexico: ACL, 2024. 583−612 [90] Wei J, Wang X Z, Schuurmans D, Bosma M, Ichter B, Xia F, et al. Chain-of-thought prompting elicits reasoning in large language models. In: Proceedings of the 36th International Conference on Neural Information Processing Systems. New Orleans, USA: Curran Associates Inc., 2022. Article No. 1800 [91] Li X P, Su L X, Jia P Y, Cheng S Q, Wang J F, Yin D W, et al. Agent4Ranking: Semantic robust ranking via personalized query rewriting using multi-agent LLMs. ACM Transactions on Information Systems, 2025, 43(6): Article No. 157 doi: 10.1145/3749099 [92] Li X H, Chen C, Zhao X Y, Zhang Y, Xing C X. E4SRec: An elegant effective efficient extensible solution of large language models for sequential recommendation. arXiv preprint arXiv: 2312.02443, 2023. [93] Wang D, Salamatian K, Xia Y Q, Deng W W, Zhang Q. BERT4CTR: An efficient framework to combine pre-trained language model with non-textual features for CTR prediction. In: Proceedings of the 29th ACM SIGKDD Conference on Knowledge Discovery and Data Mining. Long Beach, USA: ACM, 2023. 5039−5050 [94] Tang Z L, Huan Z X, Li Z H, Zhang X L, Hu J, Fu C L, et al. One model for all: Large language models are domain-agnostic recommendation systems. ACM Transactions on Information Systems, 2025, 43(5): Article No. 118 doi: 10.1145/3802983 [95] Lin J H, Shan R, Zhu C X, Du K N H, Chen B, Quan S G, et al. ReLLa: Retrieval-enhanced large language models for lifelong sequential behavior comprehension in recommendation. In: Proceedings of the ACM Web Conference. Singapore: ACM, 2024. 3497−3508 [96] Wu X S, Zhou H C, Yao W L, Huang X, Liu N H. Towards personalized cold-start recommendation with prompts. arXiv preprint arXiv: 2306.17256, 2023. [97] Prakash T, Jalan R, Singh B, Onoe N. CR-SoRec: BERT driven consistency regularization for social recommendation. In: Proceedings of the 17th ACM Conference on Recommender Systems. Singapore: ACM, 2023. 883−889 [98] Geng S J, Liu S C, Fu Z H, Ge Y Q, Zhang Y F. Recommendation as language processing (RLP): A unified pretrain, personalized prompt & predict paradigm (P5). In: Proceedings of the 16th ACM Conference on Recommender Systems. Seattle, USA: ACM, 2022. 299−315 [99] Bao K Q, Zhang J Z, Zhang Y, Wang W J, Feng F L, He X N. TALLRec: An effective and efficient tuning framework to align large language model with recommendation. In: Proceedings of the 17th ACM Conference on Recommender Systems. Singapore: ACM, 2023. 1007−1014 [100] Zhang Y, Feng F L, Zhang J Z, Bao K Q, Wang Q F, He X N. CoLLM: Integrating collaborative embeddings into large language models for recommendation. IEEE Transactions on Knowledge and Data Engineering, 2025, 37(5): 2329−2340 doi: 10.1109/tkde.2025.3540912 [101] Zhang Y, Bao K Q, Yan M, Wang W J, Feng F L, He X N. Text-like encoding of collaborative information in large language models for recommendation. In: Proceedings of the 62nd Annual Meeting of the Association for Computational Linguistics (Volume 1: Long Papers). Bangkok, Thailand: ACL, 2024. 9181−9191 [102] Lin J Y, Men R, Yang A, Zhou C, Ding M, Zhang Y C, et al. M6: A Chinese multimodal pretrainer. arXiv preprint arXiv: 2103.00823, 2021. [103] Warstadt A, Singh A, Bowman S R. Neural network acceptability judgments. Transactions of the Association for Computational Linguistics, 2019, 7: 625−641 doi: 10.1162/tacl_a_00290 [104] Touvron H, Martin L, Stone K, Albert P, Almahairi A, Babaei Y, et al. Llama 2: Open foundation and fine-tuned chat models. arXiv preprint arXiv: 2307.09288, 2023. [105] Zheng L M, Chiang W L, Sheng Y, Zhuang S Y, Wu Z H, Zhuang Y H, et al. Judging LLM-as-a-judge with MT-bench and chatbot arena. In: Proceedings of the 37th International Conference on Neural Information Processing Systems. New Orleans, USA: Curran Associates Inc., 2023. Article No. 2020 [106] Xu C W, Guo D Y, Duan N, McAuley J. Baize: An open-source chat model with parameter-efficient tuning on self-chat data. In: Proceedings of the Conference on Empirical Methods in Natural Language Processing. Singapore: ACL, 2023. 6268−6278 [107] Zhang J J, Xie R B, Hou Y P, Zhao W X, Lin L Y, Wen J R. Recommendation as instruction following: A large language model empowered recommendation approach. ACM Transactions on Information Systems, 2025, 43(5): Article No. 114 doi: 10.1145/3795143 [108] Hayet I, Yao Z J, Luo B. Invernet: An inversion attack framework to infer fine-tuning datasets through word embeddings. In: Proceedings of the Findings of the Association for Computational Linguistics. Abu Dhabi, United Arab Emirates: ACL, 2022. 5009−5018 [109] Li H R, Song Y Q, Fan L X. You don't know my favorite color: Preventing dialogue representations from revealing speakers' private personas. In: Proceedings of the Conference of the North American Chapter of the Association for Computational Linguistics: Human Language Technologies. Seattle, USA: ACL, 2022. 5858−5870 [110] Qu L, Yuan W, Zheng R Q, Cui L Z, Shi Y H, Yin H Z. Towards personalized privacy: User-governed data contribution for federated recommendation. In: Proceedings of the ACM Web Conference. Singapore, Singapore: ACM, 2024. 3910−3918 [111] Chen C, Sun F, Zhang M, Ding B L. Recommendation unlearning. In: Proceedings of the ACM Web Conference. Lyon, France: ACM, 2022. 2768−2777 [112] Li Y Y, Chen C C, Zheng X L, Liu J L, Wang J. Making recommender systems forget: Learning and unlearning for erasable recommendation. Knowledge-Based Systems, 2024, 283: Article No. 111124 doi: 10.1016/j.knosys.2023.111124 [113] Zhao J J, Wang W J, Xu C, Ren Z C, Ng S K, Chua T S. LLM-based federated recommendation. arXiv preprint arXiv: 2402.09959, 2024. [114] Wang H Y, Lin J H, Chen B, Yang Y, Tang R M, Zhang W N, et al. Towards efficient and effective unlearning of large language models for recommendation. Frontiers of Computer Science, 2025, 19(3): Article No. 193327 doi: 10.1007/s11704-024-40044-2 [115] Hu Z Y, Zhang Y, Xiao M H, Wang W J, Feng F L, He X N. Exact and efficient unlearning for large language model-based recommendation. IEEE Transactions on Knowledge and Data Engineering, 2025, 37(10): 5866−5877 doi: 10.1109/TKDE.2025.3594687 [116] Bourtoule L, Chandrasekaran V, Choquette-Choo C A, Jia H R, Travers A, Zhang B W, et al. Machine unlearning. In: Proceedings of the IEEE Symposium on Security and Privacy (SP). San Francisco, USA: IEEE, 2021. 141−159 [117] Zeng H M, Yue Z R, Jiang Q, Wang D. Federated recommendation via hybrid retrieval augmented generation. In: Proceedings of the IEEE International Conference on Big Data (BigData). Washington, USA: IEEE, 2024. 8078−8087 [118] Zhang C X, Long G D, Guo H K, Fang X, Song Y, Liu Z J, et al. Federated adaptation for foundation model-based recommendations. In: Proceedings of the 33rd International Joint Conference on Artificial Intelligence (IJCAI). Jeju, Republic of Korea: ijcai.org, 2024. 5453−5461 [119] Covington P, Adams J, Sargin E. Deep neural networks for YouTube recommendations. In: Proceedings of the 10th ACM Conference on Recommender Systems. Boston, USA: ACM, 2016. 191−198 [120] Mireshghallah F, Uniyal A, Wang T H, Evans D, Berg-Kirkpatrick T. An empirical analysis of memorization in fine-tuned autoregressive language models. In: Proceedings of the Conference on Empirical Methods in Natural Language Processing. Abu Dhabi, United Arab Emirates: ACL, 2022. 1816−1826 [121] Zhu Y T, Zhang P T, Zhang C H, Chen Y F, Xie B Y, Liu Z, et al. INTERS: Unlocking the power of large language models in search with instruction tuning. In: Proceedings of the 62nd Annual Meeting of the Association for Computational Linguistics (Volume 1: Long Papers). Bangkok, Thailand: ACL, 2024. 2782−2809 [122] Lin X Y, Wang W J, Li Y Q, Yang S, Feng F L, Wei Y W, et al. Data-efficient fine-tuning for LLM-based recommendation. In: Proceedings of the 47th International ACM SIGIR Conference on Research and Development in Information Retrieval. Washington, USA: ACM, 2024. 365−374 [123] Shokri R, Stronati M, Song C Z, Shmatikov V. Membership inference attacks against machine learning models. In: Proceedings of the IEEE Symposium on Security and Privacy (SP). San Jose, USA: IEEE, 2017. 3−18 [124] Yeom S, Giacomelli I, Fredrikson M, Jha S. Privacy risk in machine learning: Analyzing the connection to overfitting. In: Proceedings of the 31st Computer Security Foundations Symposium (CSF). Oxford, UK: IEEE, 2018. 268−282 [125] Salem A, Zhang Y, Humbert M, Berrang P, Fritz M, Backes M. ML-leaks: Model and data independent membership inference attacks and defenses on machine learning models. In: Proceedings of the 26th Annual Network and Distributed System Security Symposium. San Diego, USA: The Internet Society, 2019. [126] Wang Y J, Wang C H, Wang Z G, Zhou S L, Liu H, Bi J B, et al. Against membership inference attack: Pruning is all you need. In: Proceedings of the 30th International Joint Conference on Artificial Intelligence (IJCAI). Montreal, Canada: ijcai.org, 2021. 3141−3147 [127] Chen Q R, Xiang C, Xue M H, Li B, Borisov N, Kaarfar D, et al. Differentially private data generative models. arXiv preprint arXiv: 1812.02274, 2018. [128] Hu L, Li J, Lin G B, Peng S Y, Zhang Z X, Zhang Y Y, et al. Defending against membership inference attacks with high utility by GAN. IEEE Transactions on Dependable and Secure Computing, 2023, 20(3): 2144−2157 doi: 10.1109/TDSC.2022.3174569 [129] Goodfellow I J, Pouget-Abadie J, Mirza M, Xu B, Warde-Farley D, Ozair S, et al. Generative adversarial nets. In: Proceedings of the 28th International Conference on Neural Information Processing Systems. Montreal, Canada: MIT Press, 2014. 2672−2680 [130] He X N, He Z K, Du X Y, Chua T S. Adversarial personalized ranking for recommendation. In: Proceedings of the 41st International ACM SIGIR Conference on Research & Development in Information Retrieval. Ann Arbor, USA: ACM, 2018. 355−364 [131] Goodfellow I J, Shlens J, Szegedy C. Explaining and harnessing adversarial examples. In: Proceedings of the 3rd International Conference on Learning Representations (ICLR). San Diego, USA: OpenReview.net, 2015. [132] Yuan F, Yao L N, Benatallah B. Adversarial collaborative auto-encoder for top-N recommendation. In: Proceedings of the International Joint Conference on Neural Networks (IJCNN). Budapest, Hungary: IEEE, 2019. 1−8 [133] Yuan F, Yao L N, Benatallah B. Adversarial collaborative neural network for robust recommendation. In: Proceedings of the 42nd International ACM SIGIR Conference on Research and Development in Information Retrieval. Paris, France: ACM, 2019. 1065−1068 [134] Li R R, Li L D, Wu X, Zhou Y H, Wang W. Click feedback-aware query recommendation using adversarial examples. In: Proceedings of the World Wide Web Conference. San Francisco, USA: ACM, 2019. 2978−2984 [135] Park D H, Chang Y. Adversarial sampling and training for semi-supervised information retrieval. In: Proceedings of the World Wide Web Conference. San Francisco, USA: ACM, 2019. 1443−1453 [136] Chen H Y, Li J. Adversarial tensor factorization for context-aware recommendation. In: Proceedings of the 13th ACM Conference on Recommender Systems. Copenhagen, Denmark: ACM, 2019. 363−367 [137] Wang Q Y, Yin H Z, Chen T, Yu J L, Zhou A, Zhang X L. Fast-adapting and privacy-preserving federated recommender system. The VLDB Journal, 2022, 31(5): 877−896 doi: 10.1007/s00778-021-00700-6 [138] Wu C W, Lian D F, Ge Y, Zhu Z H, Chen E H, Yuan S C. Fight fire with fire: Towards robust recommender systems via adversarial poisoning training. In: Proceedings of the 44th International ACM SIGIR Conference on Research and Development in Information Retrieval. New York, USA: ACM, 2021. 1074−1083 [139] Wang Z L, Chen X. Robust recommendation with adversarial gaussian data augmentation. In: Proceedings of the ACM Web Conference. Austin, USA: ACM, 2023. 897−905 [140] Hu H S, Salcic Z, Sun L C, Dobbie G, Yu P S, Zhang X Y. Membership inference attacks on machine learning: A survey. ACM Computing Surveys, 2022, 54(11s): Article No. 235 [141] Bai L, Hu H B, Ye Q Q, Li H R, Wang L X, Xu J L. Membership inference attacks and defenses in federated learning: A survey. ACM Computing Surveys, 2025, 57(4): Article No. 89 [142] Niu J, Liu P, Zhu X Y, Shen K, Wang Y C, Chi H T, et al. A survey on membership inference attacks and defenses in machine learning. Journal of Information and Intelligence, 2024, 2(5): 404−454 doi: 10.1016/j.jiixd.2024.02.001 [143] Deldjoo Y, di Noia T, Merra F A. A survey on adversarial recommender systems: From attack/defense strategies to generative adversarial networks. ACM Computing Surveys, 2022, 54(2): Article No. 35 [144] Chakraborty A, Alam M, Dey V, Chattopadhyay A, Mukhopadhyay D. A survey on adversarial attacks and defences. CAAI Transactions on Intelligence Technology, 2021, 6(1): 25−45 doi: 10.1049/cit2.12028 [145] Costa J C, Roxo T, Proença H, Inácio P R M. How deep learning sees the world: A survey on adversarial attacks & defenses. IEEE Access, 2024, 12: 61113−61136 doi: 10.1109/ACCESS.2024.3395118 [146] Gunes I, Kaleli C, Bilge A, Polat H. Shilling attacks against recommender systems: A comprehensive survey. Artificial Intelligence Review, 2014, 42(4): 767−799 doi: 10.1007/s10462-012-9364-9 [147] Si M D, Li Q S. Shilling attacks against collaborative recommender systems: A review. Artificial Intelligence Review, 2020, 53(1): 291−319 doi: 10.1007/s10462-018-9655-x [148] Sundar A P, Li F, Zou X K, Gao T C, Russomanno E D. Understanding shilling attacks and their detection traits: A comprehensive survey. IEEE Access, 2020, 8: 171703−171715 doi: 10.1109/ACCESS.2020.3022962 [149] Wang Z W, Yu J L, Gao M, Yuan W, Ye G H, Sadiq S, et al. Poisoning attacks and defenses in recommender systems: A survey. arXiv preprint arXiv: 2406.01022, 2024. [150] Wang Z B, Ma J J, Wang X, Hu J H, Qin Z, Ren K. Threats to training: A survey of poisoning attacks and defenses on machine learning systems. ACM Computing Surveys, 2023, 55(7): Article No. 134 [151] Tian Z Y, Cui L, Liang J, Yu S. A comprehensive survey on poisoning attacks and countermeasures in machine learning. ACM Computing Surveys, 2023, 55(8): Article No. 166 doi: 10.1145/3551636 [152] Jia J Y, Gong N Z. Defending against machine learning based inference attacks via adversarial examples: Opportunities and challenges. Adaptive Autonomous Secure Cyber Systems. Cham: Springer, 2020. 23−40 [153] Chakraborty A, Alam M, Dey V, Chattopadhyay A, Mukhopadhyay D. Adversarial attacks and defences: A survey. arXiv preprint arXiv: 1810.00069, 2018. [154] Goyal S, Doddapaneni S, Khapra M M, Ravindran B. A survey of adversarial defenses and robustness in NLP. ACM Computing Surveys, 2023, 55(14s): Article No. 332 doi: 10.1145/3593042 [155] Ahmed S T, Vinoth K V, Mahesh T R, Narasimha P L V, Velmurugan A K, Muthukumaran V, et al. FedOPT: Federated learning-based heterogeneous resource recommendation and optimization for edge computing. Soft Computing, DOI: 10.1007/s00500-023-09542-6 [156] Li Z, Bilal M, Xu X L, Jiang J L, Cui Y. Federated learning-based cross-enterprise recommendation with graph neural networks. IEEE Transactions on Industrial Informatics, 2023, 19(1): 673−682 doi: 10.1109/TII.2022.3203395 [157] Duan S J, Zhang D Y, Wang Y B, Li L X, Zhang Y X. JointRec: A deep-learning-based joint cloud video recommendation framework for mobile IoT. IEEE Internet of Things Journal, 2020, 7(3): 1655−1666 doi: 10.1109/JIOT.2019.2944889 [158] Neumann D, Lutz A, Müller K, Samek W. A privacy preserving system for movie recommendations using federated learning. ACM Transactions on Recommender Systems, 2025, 3(2): Article No. 14 doi: 10.1145/3634686 [159] Yuan W, Yang C Q, Nguyen Q V H, Cui L Z, He T K, Yin H Z. Interaction-level membership inference attack against federated recommender systems. In: Proceedings of the ACM Web Conference. Austin, USA: ACM, 2023. 1053−1062 [160] Ali W, Kumar R, Zhou X M, Shao J. Responsible recommendation services with blockchain empowered asynchronous federated learning. ACM Transactions on Intelligent Systems and Technology, 2024, 15(4): Article No. 78 doi: 10.1145/3633520 [161] Feng Y, Qi Y Q, Li H Z, Wang X X, Tian J X. Leveraging federated learning and edge computing for recommendation systems within cloud computing networks. In: Proceedings of the 3rd International Symposium on Computer Applications and Information Systems (ISCAIS). Wuhan, China: SPIE, 2024. Article No. 1321012 [162] Polat H, Du W L. Privacy-preserving collaborative filtering using randomized perturbation techniques. In: Proceedings of the 3rd IEEE International Conference on Data Mining. Melbourne, USA: IEEE, 2003. 625−628 [163] McSherry F, Mironov I. Differentially private recommender systems: Building privacy into the Netflix Prize contenders. In: Proceedings of the 15th ACM SIGKDD International Conference on Knowledge Discovery and Data Mining. Paris, France: ACM, 2009. 627−636 [164] Shin H, Kim S, Shin J, Xiao X K. Privacy enhanced matrix factorization for recommendation with local differential privacy. IEEE Transactions on Knowledge and Data Engineering, 2018, 30(9): 1770−1782 doi: 10.1109/tkde.2018.2805356 [165] Müllner P, Lex E, Schedl M, Kowald D. ReuseKNN: Neighborhood reuse for differentially private KNN-based recommendations. ACM Transactions on Intelligent Systems and Technology, 2023, 14(5): Article No. 80 doi: 10.1145/3608481 [166] Koren Y, Bell R, Volinsky C. Matrix factorization techniques for recommender systems. Computer, 2009, 42(8): 30−37 doi: 10.18297/etd/3661 [167] Berlioz A, Friedman A, Kaafar M A, Boreli R, Berkovsky S. Applying differential privacy to matrix factorization. In: Proceedings of the 9th ACM Conference on Recommender Systems. Vienna, Austria: ACM, 2015. 107−114 [168] Friedman A, Berkovsky S, Kaafar M A. A differential privacy framework for matrix factorization recommender systems. User Modeling and User-Adapted Interaction, 2016, 26(5): 425−458 doi: 10.1007/s11257-016-9177-7 [169] Jorgensen Z, Yu T, Cormode G. Conservative or liberal? Personalized differential privacy. In: Proceedings of the 31st International Conference on Data Engineering. Seoul, Republic of Korea: IEEE, 2015. 1023−1034 [170] Johnson W B, Lindenstrauss J, Schechtman G. Extensions of Lipschitz maps into Banach spaces. Israel Journal of Mathematics, 1986, 54(2): 129−138 doi: 10.1007/BF02764938 [171] Meng X Y, Wang S H, Shu K, Li J D, Chen B, Liu H, et al. Personalized privacy-preserving social recommendation. In: Proceedings of the 32nd AAAI Conference on Artificial Intelligence. New Orleans, USA: AAAI Press, 2018. 3796−3803 [172] Zhu X, Sun Y Q. Differential privacy for collaborative filtering recommender algorithm. In: Proceedings of the ACM on International Workshop on Security and Privacy Analytics. New Orleans, USA: ACM, 2016. 9−16 [173] Machanavajjhala A, Korolova A, das Sarma A. Personalized social recommendations: Accurate or private. Proceedings of the VLDB Endowment, 2011, 4(7): 440−450 doi: 10.14778/1988776.1988780 [174] Zhu T Q, Ren Y L, Zhou W L, Rong J, Xiong P. An effective privacy preserving algorithm for neighborhood-based collaborative filtering. Future Generation Computer Systems, 2014, 36: 142−155 doi: 10.1016/j.future.2013.07.019 [175] Shen Y L, Jin H X. Privacy-preserving personalized recommendation: An instance-based approach via differential privacy. In: Proceedings of the IEEE International Conference on Data Mining. Shenzhen, China: IEEE, 2014. 540−549 [176] Jorgensen Z, Yu T. A privacy-preserving framework for personalized, social recommendations. In: Proceedings of the 17th International Conference on Extending Database Technology (EDBT). Athens, Greece: OpenProceedings.org, 2014. 571−582 [177] Gentry C. Fully homomorphic encryption using ideal lattices. In: Proceedings of the 41st Annual ACM Symposium on Theory of Computing. Bethesda, USA: ACM, 2009. 169−178 [178] Canny J. Collaborative filtering with privacy. In: Proceedings of the IEEE Symposium on Security and Privacy. Berkeley, USA: IEEE, 2002. 45−57 [179] Goldreich O. Secure multi-party computation. Manuscript Preliminary Version, 1998, 78(110): 1−108 [180] Shamir A. How to share a secret. Communications of the ACM, 1979, 22(11): 612−613 doi: 10.1145/359168.359176 [181] Li D S, Chen C, Lv Q, Shang L, Zhao Y Y, Lu T, et al. An algorithm for efficient privacy-preserving item-based collaborative filtering. Future Generation Computer Systems, 2016, 55: 311−320 doi: 10.1016/j.future.2014.11.003 [182] Nakamoto S. Bitcoin: A peer-to-peer electronic cash system [Online], available: https://nakamotoinstitute.org/library/bitcoin/, October 27, 2026 [183] Patel S B, Bhattacharya P, Tanwar S, Kumar N. KiRTi: A blockchain-based credit recommender system for financial institutions. IEEE Transactions on Network Science and Engineering, 2021, 8(2): 1044−1054 doi: 10.1109/TNSE.2020.3005678 [184] Wang S, Huang C C, Li J J, Yuan Y, Wang F Y. Decentralized construction of knowledge graphs for deep recommender systems based on blockchain-powered smart contracts. IEEE Access, 2019, 7: 136951−136961 doi: 10.1109/ACCESS.2019.2942338 [185] Mantey E A, Zhou C H, Anajemba J H, Hamid Y, Arthur J K. Blockchain-enabled technique for privacy-preserved medical recommender system. IEEE Access, 2023, 11: 40944−40953 doi: 10.1109/ACCESS.2023.3267431 [186] 胡甜媛, 李泽成, 李必信, 包骐豪. 智能合约的合约安全和隐私安全研究综述. 计算机学报, 2021, 44(12): 2485−2514 doi: 10.11897/SP.J.1016.2021.02485Hu Tian-Yuan, Li Ze-Cheng, Li Bi-Xin, Bao Qi-Hao. Contractual security and privacy security of smart contract: A system mapping study. Chinese Journal of Computers, 2021, 44(12): 2485−2514 doi: 10.11897/SP.J.1016.2021.02485 [187] Xu J L, Lin J, Liang W, Li K C. Privacy preserving personalized blockchain reliability prediction via federated learning in IoT environments. Cluster Computing, 2022, 25(4): 2515−2526 doi: 10.1007/s10586-021-03399-w [188] Teimoori Z, Yassine A, Hossain M S. A secure cloudlet-based charging station recommendation for electric vehicles empowered by federated learning. IEEE Transactions on Industrial Informatics, 2022, 18(9): 6464−6473 doi: 10.1109/TII.2022.3148997 [189] Jiang X Y, Liu B S, Qin J C, Zhang Y C, Qian J B. FedNCF: Federated neural collaborative filtering for privacy-preserving recommender system. In: Proceedings of the International Joint Conference on Neural Networks (IJCNN). Padua, Italy: IEEE, 2022. 1−8 [190] Hu R, Guo Y X, Gong Y M. Federated learning with sparsified model perturbation: Improving accuracy under client-level differential privacy. IEEE Transactions on Mobile Computing, 2024, 23(8): 8242−8255 doi: 10.1109/TMC.2023.3343288 [191] 汤凌韬, 陈左宁, 张鲁飞, 吴东. 联邦学习中的隐私问题研究进展. 软件学报, 2023, 34(1): 197−229 doi: 10.13328/j.cnki.jos.006411Tang Ling-Tao, Chen Zuo-Ning, Zhang Lu-Fei, Wu Dong. Research progress of privacy issues in federated learning. Journal of Software, 2023, 34(1): 197−229 doi: 10.13328/j.cnki.jos.006411 [192] 刘艺璇, 陈红, 刘宇涵, 李翠平. 联邦学习中的隐私保护技术. 软件学报, 2022, 33(3): 1057−1092 doi: 10.13328/j.cnki.jos.006446Liu Yi-Xuan, Chen Hong, Liu Yu-Han, Li Cui-Ping. Privacy-preserving techniques in federated learning. Journal of Software, 2022, 33(3): 1057−1092 doi: 10.13328/j.cnki.jos.006446 [193] 朱建明, 张沁楠, 高胜, 丁庆洋, 袁丽萍. 基于区块链的隐私保护可信联邦学习模型. 计算机学报, 2021, 44(12): 2464−2484 doi: 10.11897/sp.j.1016.2001.02464Zhu Jian-Ming, Zhang Qin-Nan, Gao Sheng, Ding Qing-Yang, Yuan Li-Ping. Privacy preserving and trustworthy federated learning model based on blockchain. Chinese Journal of Computers, 2021, 44(12): 2464−2484 doi: 10.11897/sp.j.1016.2001.02464 [194] Mantey E A, Zhou C H, Anajemba J H, Arthur J K, Hamid Y, Chowhan A, et al. Federated learning approach for secured medical recommendation in internet of medical things using homomorphic encryption. IEEE Journal of Biomedical and Health Informatics, 2024, 28(6): 3329−3340 doi: 10.1109/JBHI.2024.3350232 [195] Mai P H, Pang Y. Privacy-preserving Multiview matrix factorization for recommender systems. IEEE Transactions on Artificial Intelligence, 2024, 5(1): 267−277 doi: 10.1109/TAI.2023.3240700 [196] Ouyang L, Wu J, Jiang X, Almeida D, Wainwright C L, Mishkin P, et al. Training language models to follow instructions with human feedback. In: Proceedings of the 36th International Conference on Neural Information Processing Systems. New Orleans, USA: Curran Associates Inc., 2022. Article No. 2011 [197] Yu S X, Muñoz J P, Jannesari A. Federated foundation models: Privacy-preserving and collaborative learning for large models. In: Proceedings of the Joint International Conference on Computational Linguistics, Language Resources and Evaluation (LREC-COLING). Torino, Italia: ELRA and ICCL, 2024. 7174−7184 [198] Miranda M, Ruzzetti E S, Santilli A, Zanzotto F M, Bratières S, Rodolà E. Preserving privacy in large language models: A survey on current threats and solutions. arXiv preprint arXiv: 2408.05212, 2024. [199] Salas J. Sanitizing and measuring privacy of large sparse datasets for recommender systems. Journal of Ambient Intelligence and Humanized Computing, 2023, 14(11): 15073−15084 doi: 10.1007/s12652-019-01391-2 [200] Mandal B, Amariucai G, Wei S Q. Initial exploration of zero-shot privacy utility tradeoffs in tabular data using GPT-4. In: Proceedings of the International Joint Conference on Neural Networks (IJCNN). Yokohama, Japan: IEEE, 2024. 1−8 [201] Zhang J Y, Vahidian S, Kuo M, Li C Y, Zhang R Y, Yu T, et al. Towards building the federatedgpt: Federated instruction tuning. In: Proceedings of the IEEE International Conference on Acoustics, Speech and Signal Processing (ICASSP). Seoul, Republic of Korea: IEEE, 2024. 6915−6919 [202] Fan T, Kang Y, Ma G Q, Chen W J, Wei W B, Fan L X, et al. FATE-LLM: A industrial grade federated learning framework for large language models. arXiv preprint arXiv: 2310.10049, 2023. [203] Behnia R, Ebrahimi M R, Pacheco J, Padmanabhan B. EW-tune: A framework for privately fine-tuning large language models with differential privacy. In: Proceedings of the IEEE International Conference on Data Mining Workshops (ICDMW). Orlando, USA: IEEE, 2022. 560−566 [204] Wu X W, Gong L, Xiong D Y. Adaptive differential privacy for language model training. In: Proceedings of the 1st Workshop on Federated Learning for Natural Language Processing (FL4NLP). Dublin, Ireland: ACL, 2022. 21−26 [205] Chen J A, Yang D Y. Unlearn what you want to forget: Efficient unlearning for LLMs. In: Proceedings of the Conference on Empirical Methods in Natural Language Processing. Singapore: ACL, 2023. 12041−12052 [206] Jang J, Yoon D, Yang S, Cha S, Lee M, Logeswaran L, et al. Knowledge unlearning for mitigating privacy risks in language models. In: Proceedings of the 61st Annual Meeting of the Association for Computational Linguistics (Volume 1: Long Papers). Toronto, Canada: ACL, 2023. 14389−14408 [207] Liu Z, Kalinli O. Forgetting private textual sequences in language models via leave-one-out ensemble. In: Proceedings of the IEEE International Conference on Acoustics, Speech and Signal Processing (ICASSP). Seoul, Republic of Korea: IEEE, 2024. 10261−10265 [208] Pochinkov N, Schoots N. Dissecting language models: Machine unlearning via selective pruning. arXiv preprint arXiv: 2403.01267, 2024. [209] Ilharco G, Ribeiro M T, Wortsman M, Schmidt L, Hajishirzi H, Farhadi A. Editing models with task arithmetic. In: Proceedings of the 11th International Conference on Learning Representations (ICLR). Kigali, Rwanda: OpenReview.net, 2023. [210] Liu Z Y, Dou G Y, Tan Z X, Tian Y J, Jiang M. Towards safer large language models through machine unlearning. In: Proceedings of the Findings of the Association for Computational Linguistics. Bangkok, Thailand: ACL, 2024. 1817−1829 [211] Majmudar J, Dupuy C, Peris C, Smaili S, Gupta R, Zemel R. Differentially private decoding in large language models. arXiv preprint arXiv: 2205.13621, 2022. [212] Du M X, Yue X, Chow S S M, Wang T H, Huang C Y, Sun H. DP-forward: Fine-tuning and inference on language models with differential privacy in forward pass. In: Proceedings of the ACM SIGSAC Conference on Computer and Communications Security. Copenhagen, Denmark: ACM, 2023. 2665−2679 [213] Chen T Y, Bao H B, Huang S H, Dong L, Jiao B X, Jiang D X, et al. THE-X: Privacy-preserving transformer inference with homomorphic encryption. In: Proceedings of the Findings of the Association for Computational Linguistics. Dublin, Ireland: ACL, 2022. 3510−3520 [214] Lu W J, Huang Z C, Gu Z, Li J Y, Liu J, Hong C, et al. Bumblebee: Secure two-party inference framework for large transformers. In: Proceedings of the 32nd Annual Network and Distributed System Security Symposium (NDSS). San Diego, USA: The Internet Society, 2025. [215] Ding Y C, Guo H, Guan Y W, Liu W X, Huo J R, Guan Z Y, et al. East: Efficient and accurate secure transformer framework for inference. arXiv preprint arXiv: 2308.09923, 2023. [216] Tharwat A. Classification assessment methods. Applied Computing and Informatics, 2021, 17(1): 168−192 doi: 10.1016/j.aci.2018.08.003 [217] Hinton G, Vinyals O, Dean J. Distilling the knowledge in a neural network. arXiv preprint arXiv: 1503.02531, 2015. [218] Tirkel A Z, Rankin G A, van Schyndel R M, Ho W J, Mee N R A, Osborne C F. Electronic water mark. In: Proceedings of the Digital Image Computing, Technology and Applications (DICTA). Sydney, Australia, 1993. 666−673 [219] Cao Y H, Li S Y, Liu Y X, Yan Z L, Dai Y T, Yu P S, et al. A comprehensive survey of AI-generated content (AIGC): A history of generative AI from GAN to ChatGPT. arXiv preprint arXiv: 2303.04226, 2023. [220] Wang T, Zhang Y S, Qi S R, Zhao R Y, Xia Z H, Weng J. Security and privacy on generative data in AIGC: A survey. ACM Computing Surveys, 2025, 57(4): Article No. 82 doi: 10.1145/3703626 [221] Chen C, Wu Z P, Lai Y Y, Ou W L, Liao T C, Zheng Z B. Challenges and remedies to privacy and security in AIGC: Exploring the potential of privacy computing, blockchain, and beyond. arXiv preprint arXiv: 2306.00419, 2023. [222] Zhang S J, Yuan W, Yin H Z. Comprehensive privacy analysis on federated recommender system against attribute inference attacks. IEEE Transactions on Knowledge and Data Engineering, 2024, 36(3): 987−999 doi: 10.1109/TKDE.2023.3295601 [223] Aïmeur E, Brassard G, Fernandez J M, Mani O F S. ALA-MBIC: A privacy-preserving recommender system for electronic commerce. International Journal of Information Security, 2008, 7(5): 307−334 doi: 10.1007/s10207-007-0049-3 [224] Ghazinour K, Matwin S, Sokolova M. YOURPRIVACYPROTECTOR, A recommender system for privacy settings in social networks. arXiv preprint arXiv: 1602.01937, 2016. [225] Javeed D, Saeed M S, Kumar P, Jolfaei A, Islam S, Islam A K M N. Federated learning-based personalized recommendation systems: An overview on security and privacy challenges. IEEE Transactions on Consumer Electronics, 2024, 70(1): 2618−2627 doi: 10.1109/TCE.2023.3318754 [226] Jiang J Y, Li C T, Lin S D. Towards a more reliable privacy-preserving recommender system. Information Sciences, 2019, 482: 248−265 doi: 10.1016/j.ins.2018.12.085 [227] Hu Q, Song Y Q. User consented federated recommender system against personalized attribute inference attack. In: Proceedings of the 17th ACM International Conference on Web Search and Data Mining. Merida, Mexico: ACM, 2024. 276−285 [228] Xin Y, Jaakkola T. Controlling privacy in recommender systems. In: Proceedings of the 28th International Conference on Neural Information Processing Systems. Montreal, Canada: MIT Press, 2014. 2618−2626 [229] Sinha R, Swearingen K. The role of transparency in recommender systems. In: Proceedings of the Human Factors in Computing Systems. Minneapolis, USA: ACM, 2002. 830−831 [230] Regulation P. General data protection regulation. InTouch, 2018, 25: 1−5 [231] Kayaalp M. Patient privacy in the era of big data. Balkan Medical Journal, 2018, 35(1): 8−17 doi: 10.4274/balkanmedj.2017.0966 [232] Price W N, Cohen I G. Privacy in the age of medical big data. Nature Medicine, 2019, 25(1): 37−43 doi: 10.1038/s41591-018-0272-7 [233] Alpert S A. Protecting medical privacy: Challenges in the age of genetic information. Journal of Social Issues, 2003, 59(2): 301−322 doi: 10.1111/1540-4560.00066 [234] Li M, Zeng Y M, Guo Y, Guo Y. A movie recommendation system based on differential privacy protection. Security and Communication Networks, 2020, 2020: Article No. 6611463 [235] Li M, Zeng Y M, Guo Y, Guo Y. The movie recommendation system based on differential privacy. In: Proceedings of the 6th International Symposium on Security and Privacy in Social Networks and Big Data. Tianjin, China: Springer, 2020. 318−328 [236] Nehf J P. Shopping for privacy on the internet. Journal of Consumer Affairs, 2007, 41(2): 351−375 doi: 10.1111/j.1745-6606.2007.00085.x [237] Virupaksha S, Gavini D, Venkatesulu D. Data privacy in online shopping. Computer Communication, Networking and Internet Security. Singapore: Springer, 2017. 199−207 [238] Guo D H, Chen H X, Wu R L, Wang Y G. AIGC challenges and opportunities related to public safety: A case study of ChatGPT. Journal of Safety Science and Resilience, 2023, 4(4): 329−339 doi: 10.1016/j.jnlssr.2023.08.001 [239] Bang J, Lee B T, Park P. Examination of ethical principles for LLM-based recommendations in conversational AI. In: Proceedings of the International Conference on Platform Technology and Service (PlatCon). Busan, Republic of Korea: IEEE, 2023. 109−113 [240] Liu X M, Xie L H, Wang Y P, Zou J, Xiong J B, Ying Z B, et al. Privacy and security issues in deep learning: A survey. IEEE Access, 2021, 9: 4566−4593 doi: 10.1109/ACCESS.2020.3045078 [241] Novelli C, Taddeo M, Floridi L. Accountability in artificial intelligence: What it is and how it works. AI & Society, 2024, 39(4): 1871−1882 doi: 10.1007/s00146-023-01635-y -

 下载:

计量
- 文章访问数: 168
- HTML全文浏览量: 63
- 被引次数: 0
